Open-source vulnerability management. One binary. No Docker tax.
RiskRancher ingests Qualys, Nessus, Trivy, or any scanner export through a no-code Adapter Builder, then tracks remediation in an air-gapped ticket dashboard — without Postgres, Redis, or a Kubernetes hobby project.
Download RiskRancherView on GitHub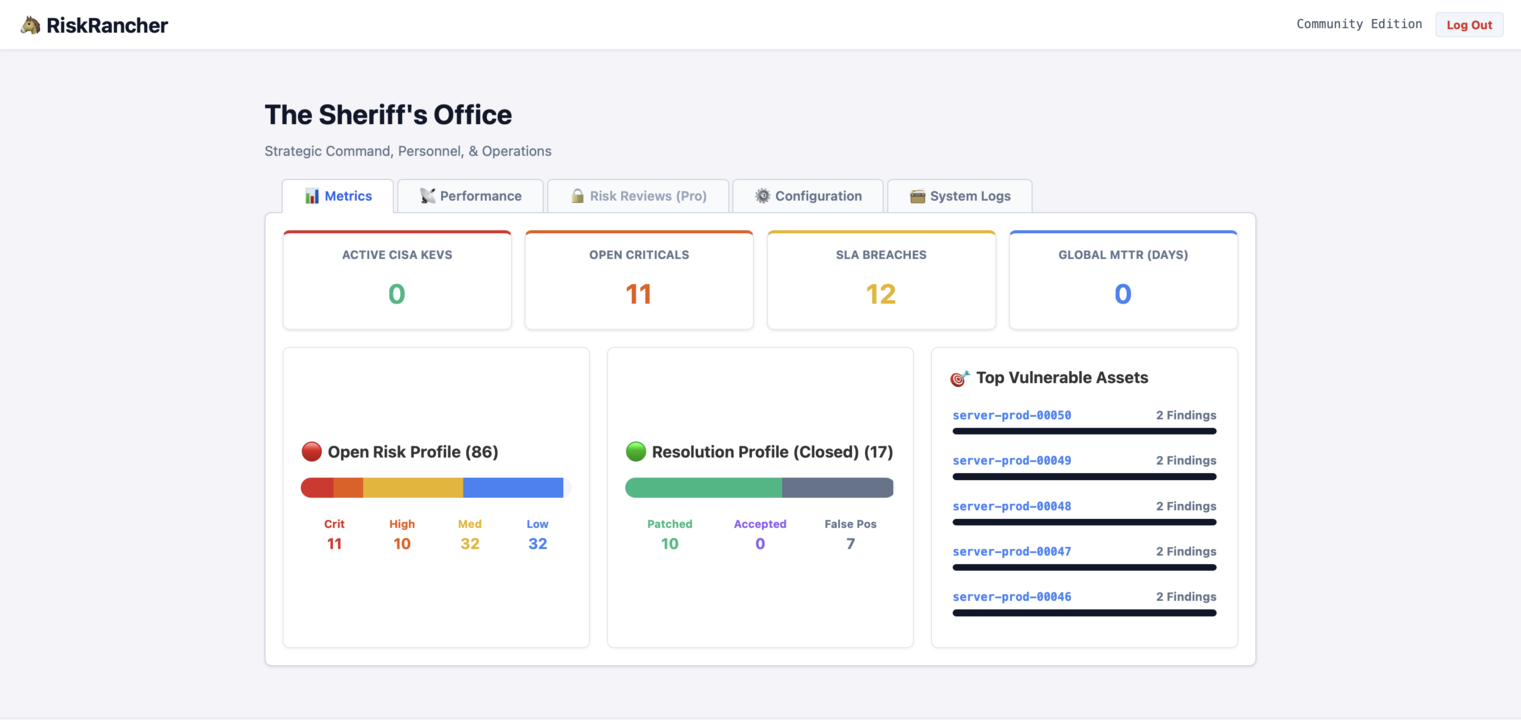
Stop writing glue code for every scanner.
The painful part of vulnerability management isn't finding issues — it's normalizing every tool's JSON into something your team can actually work. RiskRancher does that in the UI.
No-code Adapter Builder
Map any scanner in the UI — no custom parsers.
Upload a Qualys, Nessus, Trivy, Dependabot, or any JSON/CSV export. Point at the findings array, map title / asset / severity, save the adapter, and ingest. No one-off Python scripts. No waiting on an integration roadmap.
100% Air-Gapped
Your findings never leave your machine.
Single Go binary — no microservices, no Docker Compose fleet.
Embedded SQLite database on your disk. Completely offline.
Zero telemetry. Zero outbound API calls. Audit-friendly by design.
Ticket workflow
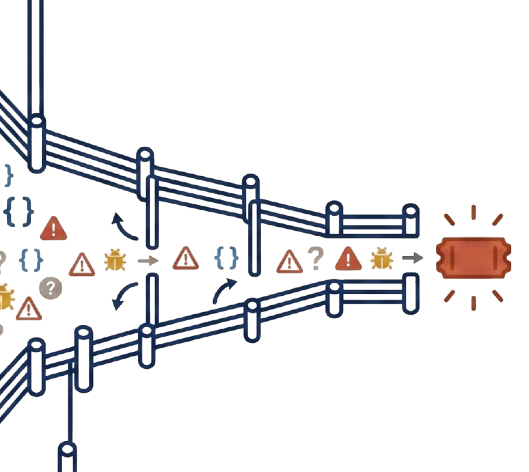
Group findings by asset and get them fixed.
Deduplicate noise into manageable tickets, track severity and SLA status, and keep security and engineering in one place — so scanner output becomes remediation work, not another spreadsheet.
Free and open source
There is no Pro tier. There is one binary.
Everything that used to be sold separately ships in the download, under the Apache 2.0 license, with no license key and no account: the auto-assign rules engine, exception pipelines with magic links for IT and Legal, suppression lists, pentest engagements with branded reports, KEV flags, SLA clocks and the audit trail.